Introduction
When businesses ask, what is a firewall, they are really asking how to protect their data, systems, and operations from constant cyber threats.
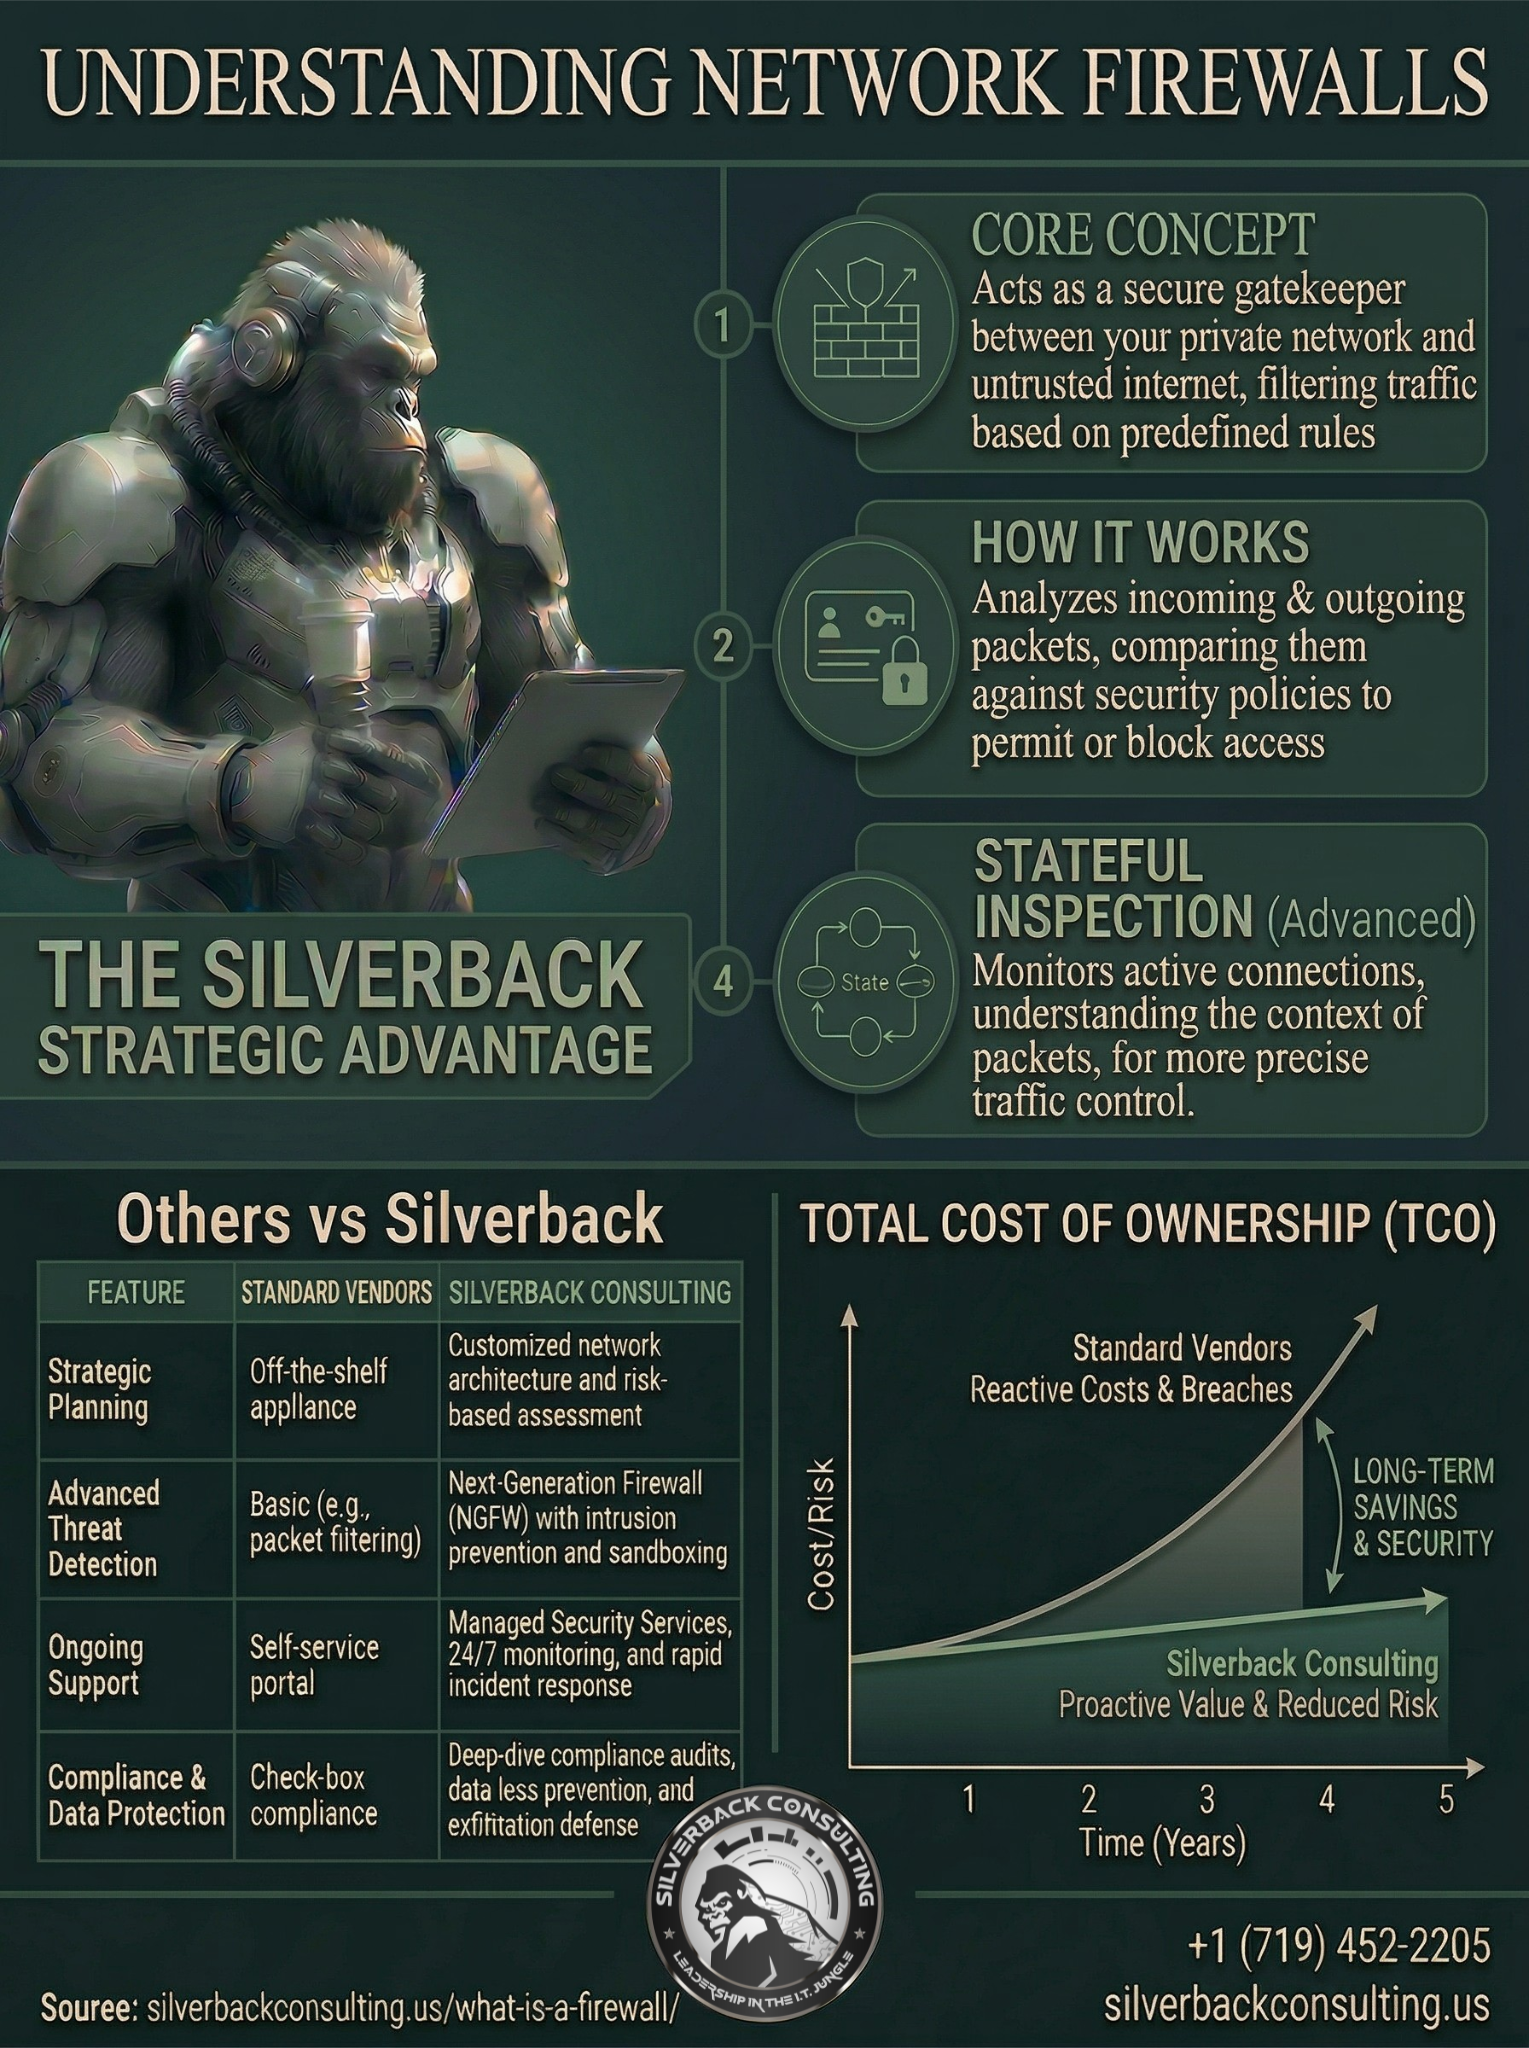
A firewall is a security system that monitors and controls incoming and outgoing network traffic based on predetermined security rules. It acts as a barrier between trusted internal networks and untrusted external sources, such as the internet.
In a world where ransomware, phishing, and zero-day exploits are increasingly sophisticated, understanding what a firewall is cannot be optional, it is foundational.
We implement firewalls not just as a tool, but as a core layer in a defense-in-depth cybersecurity strategy.
What Is a Firewall? (Complete Guide for Businesses) ▼
At its core, a firewall inspects data packets traveling across a network. But how does that translate into real protection?
A firewall:
- Analyzes traffic based on rules (IP addresses, ports, protocols)
- Allows or blocks traffic depending on those rules
- Logs activity for visibility and compliance
- Prevents unauthorized access to internal systems
Modern firewalls go far beyond simple filtering. They incorporate deep packet inspection (DPI), intrusion prevention systems (IPS), and even AI-driven threat detection to identify suspicious behavior in real time.
So, when evaluating what is a firewall, we are really talking about a dynamic security gatekeeper that adapts to evolving threats.
Not all firewalls are created equally. Choosing the right type depends on your infrastructure, risk profile, and business needs.
1. Packet-Filtering Firewalls
These are the most basic types.
They:
- Inspect packets at a surface level
- Allow or block traffic based on IP address and port rules
While fast and efficient, they lack deeper inspection capabilities.
2. Stateful Inspection Firewalls
These track the state of active connections and make decisions based on the context of traffic, not just individual packets. This provides stronger security than basic filtering.
3. Next-Generation Firewalls (NGFW)
This is where modern cybersecurity lives.
NGFWs include:
- Application awareness
- Intrusion prevention
- Advanced malware detection
- Encrypted traffic inspection
For businesses serious about protection, NGFWs are essential.
4. Cloud Firewalls (FWaaS)
As companies move to the cloud, firewalls follow.
These provide:
- Scalable, cloud-based protection
- Centralized policy management
- Protection for remote and hybrid workforces
If you’re still wondering what a firewall is in practical terms, consider the threats it actively blocks:
- Unauthorized access attempts
- Malware and ransomware traffic
- Botnet communications
- Data exfiltration attempts
- Denial-of-service (DoS) attacks
Firewalls don’t just block threats—they reduce your attack surface and give your organization visibility into what’s happening across your network.
Absolutely. In fact, the need has expanded.
With:
- Remote work
- Cloud applications
- Mobile devices
- Third-party integrations
Your network perimeter is no longer a single boundary. Firewalls now operate in a distributed security model, protecting:
- On-premise infrastructure
- Cloud environments
- Endpoints and remote users
Understanding what is a firewall today means recognizing its role in a Zero Trust architecture, where nothing is trusted by default.
This is one of the most common follow-up questions.
Hardware Firewalls
- Installed at the network perimeter
- Protect entire networks
- Ideal for business environments
Software Firewalls
- Installed on individual devices
- Provide endpoint-level protection
- Common in personal and small business use
The strongest approach combines both, creating layered security.
A firewall is not a standalone solution—it is part of a broader ecosystem.
We integrate firewalls with:
- Endpoint Detection and Response (EDR)
- Security Information and Event Management (SIEM)
- Multi-Factor Authentication (MFA)
- Security awareness training
This layered approach ensures that even if one control fails, others are in place to detect, contain, and respond.
Technology alone cannot stop every threat. That’s where the human firewall comes in.
Your employees are often the first line of defense against:
- Phishing emails
- Social engineering attacks
- Credential theft
By training staff to recognize and respond to threats, you strengthen your overall security posture. Learn more about building a strong human firewall here:
https://silverbackconsulting.us/the-human-firewall/
If you’re evaluating solutions after learning what is a firewall, focus on capabilities that deliver real protection:
- Real-time threat intelligence
- Deep packet inspection
- SSL/TLS decryption
- Intrusion prevention
- Application control
- User identity awareness
- Centralized management
The right firewall should not just block threats—it should provide visibility, control, and actionable insights.
A poorly configured firewall can create a false sense of security.
Key indicators of effective configuration:
- Strict access control policies
- Regular rule audits
- Continuous monitoring and logging
- Timely firmware and signature updates
- Integration with broader security tools
Misconfigurations are one of the most common vulnerabilities we see in business environments.
Understanding what a firewall is also means understanding what not to do.
Common mistakes include:
- Leaving default settings unchanged
- Allowing overly broad access rules
- Failing to monitor logs
- Not updating firmware regularly
- Treating the firewall as a “set it and forget it” solution
Firewalls require active management and continuous optimization.
At Silverback Consulting, we don’t just deploy firewalls—we design comprehensive security architectures tailored to your business.
We:
- Assess your current environment
- Identify vulnerabilities and gaps
- Implement enterprise-grade firewall solutions
- Continuously monitor and optimize performance
- Align your security with compliance requirements
If you’re still asking what a firewall is, the better question is: Is your firewall actually protecting your business the way it should?
A firewall is no longer just a barrier—it is an intelligent security control that plays a critical role in defending against modern cyber threats. From small businesses to enterprise environments, understanding what a firewall is, is essential for maintaining secure, resilient, and compliant operations.
The organizations that treat firewalls as a strategic asset, rather than a basic tool, are the ones that stay ahead of evolving threats.
A next generation firewall is an advanced security solution that goes beyond basic traffic filtering by providing deep packet inspection, intrusion prevention, application awareness, and real-time threat intelligence to protect modern networks.
Firewall services differ from antivirus software in that firewalls control and monitor network traffic to block unauthorized access, while antivirus software focuses on detecting and removing malicious programs on individual devices.
A firewall network refers to the placement of a firewall within a network to monitor, filter, and control traffic between internal systems and external sources like the internet.
To choose the right network defense for a small business, you need to evaluate your risk level, number of users, remote access needs, and whether a managed security provider can offer continuous monitoring and support.
A firewall in a computer is a security system that monitors and controls incoming and outgoing traffic on a device or network to prevent unauthorized access and cyber threats.
Several companies offer managed firewall services for remote teams, including providers like SilverbackConsulting.us, which deliver monitoring, configuration, and ongoing threat management tailored to distributed work environments.
A managed security service offers protection through continuous monitoring, threat detection, incident response, vulnerability management, and proactive defense strategies to keep systems secure.
A virtual firewall is a software-based firewall that operates in cloud or virtualized environments, providing scalable and flexible network protection without requiring physical hardware.
A firewall is used to protect networks and systems by controlling traffic, blocking unauthorized access, and reducing the risk of cyberattacks.
The differences between software firewalls and hardware firewalls lie in their deployment and scope, as software firewalls protect individual devices while hardware firewalls secure entire networks at the perimeter.
A firewall in networking is a security mechanism that filters and monitors data traffic between networks to ensure only safe and authorized communication is allowed.
Is Your Firewall Actually Protecting Your Business?
A firewall is only as strong as its configuration and management. If you’re unsure whether your network is truly secure, it’s time to take a closer look. At Silverback Consulting, we help businesses identify gaps, strengthen defenses, and stay ahead of evolving cyber threats. Call us today at (719) 452-2205 to speak with a cybersecurity expert and get the protection your business deserves.
Silverback Consulting
303 South Santa Fe Ave
Pueblo, CO 81003
support@silverbackconsulting.us
“Leadership in the I.T. Jungle”